For modern businesses operating in the digital landscape, handling customer information carelessly is no longer just a reputation risk—it is a direct threat to corporate survival. As regulatory frameworks tighten across the GCC, organizations face unprecedented scrutiny regarding how they collect, store, and process sensitive information. Ignoring these mandates can result in devastating financial consequences, operational paralysis, and severe legal liabilities for corporate executives.
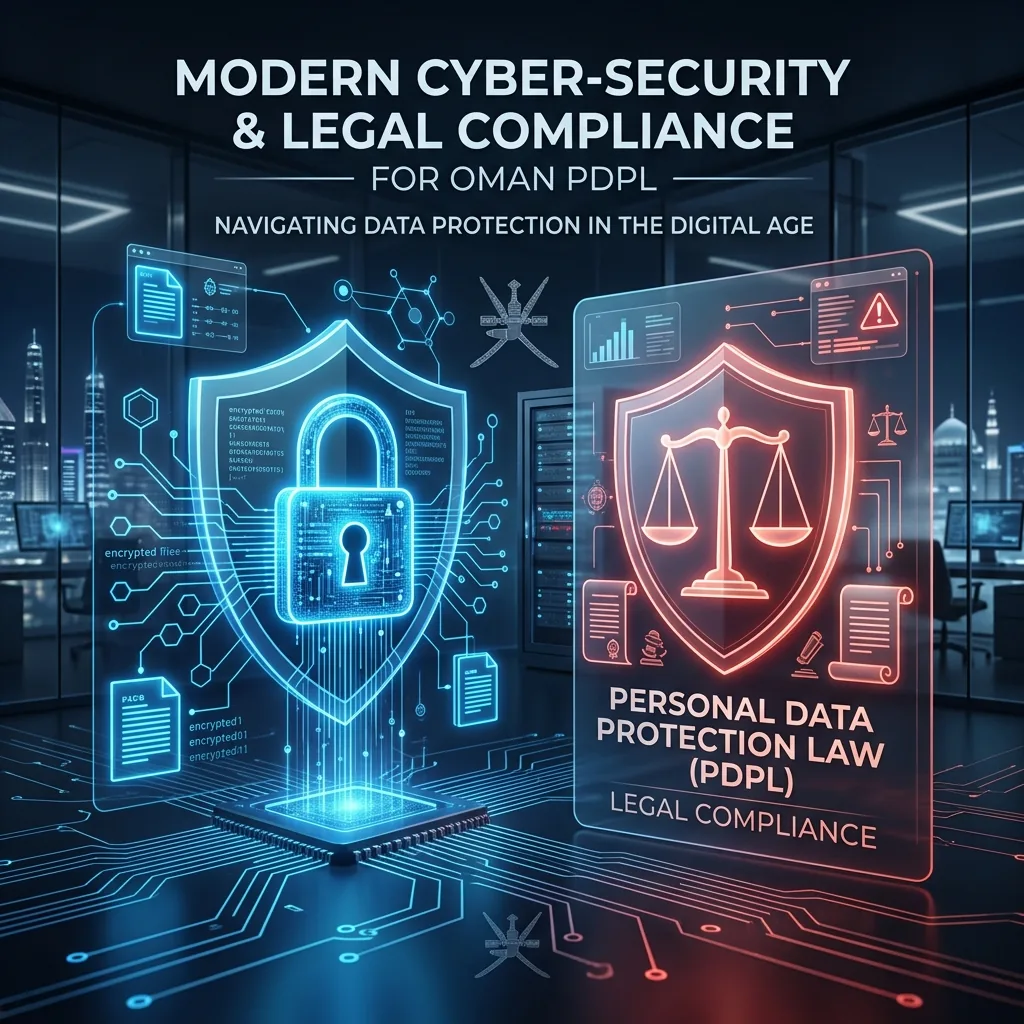
When the Sultanate implemented the Personal Data Protection Law (PDPL) via Royal Decree No. 6/2022, it signaled a fundamental shift in the regional digital economy. Designed to align with Oman Vision 2040's goals of building a secure and trusted digital society, this legislation imposes strict obligations on both data controllers and processors. Whether you are running a boutique e-commerce store in Muscat or managing logistics in Salalah, understanding the precise penalties for non-compliance is critical for risk management.
What are the financial penalties for violating Oman's PDPL?
The financial penalties for violating Oman's PDPL involve substantial monetary fines designed to deter negligence. Severe violations can trigger penalties of up to 500,000 OMR, depending on the nature of the breach and the sensitivity of the exposed data.
The regulatory authority, the Ministry of Transport, Communications and Information Technology (MTCIT), is empowered to levy fines that reflect the severity of the infraction. For example, failing to obtain explicit consent before processing sensitive personal data (such as health records or genetic information) attracts the harshest financial penalties. In contrast, administrative failures, such as neglecting to maintain proper processing records, might incur lower, yet still significant, fines. The structure ensures that businesses of all sizes treat data privacy with the utmost seriousness, as a fine of 500,000 OMR could easily bankrupt small to medium enterprises operating within the region.
Can executives face imprisonment for data breaches in Oman?
Yes, executives can face imprisonment for data breaches in Oman. The PDPL stipulates that intentional violations, gross negligence, or illegal trading of personal data can result in prison sentences ranging from several months to years.
Unlike some international frameworks that only target the corporate entity, Oman's legal structure holds individuals accountable. If a CEO, CTO, or Data Protection Officer is found to have knowingly bypassed security protocols or sold customer data for profit, the corporate veil will not protect them from criminal prosecution. This dual-threat of corporate fines and personal imprisonment makes executive oversight a non-negotiable aspect of daily operations. Board members must actively ensure that sufficient budgets are allocated for cybersecurity infrastructure to defend against potential breaches and subsequent legal action.
How does non-compliance affect business operations in the GCC?
Non-compliance affects business operations by triggering immediate regulatory audits, potential suspension of data processing activities, and severe reputational damage. Companies may be legally blocked from handling customer data until security flaws are entirely remediated.
Beyond the direct financial fines, the operational costs of a data breach are staggering. Under the PDPL, if an organization in Sohar suffers a breach due to inadequate security measures, the MTCIT has the authority to halt their data processing capabilities. For an e-commerce platform, this effectively means they cannot process orders, manage accounts, or operate their business. Furthermore, the mandatory requirement to notify affected customers creates a public relations crisis. Trust is hard to build and easy to lose; consumers are increasingly hesitant to engage with brands that demonstrate a disregard for their privacy. Restoring that trust often requires investing millions in rebranding and enhanced security protocols, far exceeding the cost of initial compliance.
To mitigate these risks, organizations must adopt a proactive rather than reactive stance. Implementing robust encryption standards, conducting regular vulnerability assessments, and training staff on phishing threats are foundational steps. As Oman continues to modernize its digital infrastructure under Vision 2040, aligning with the PDPL is not merely a legal obligation, but a strategic advantage that demonstrates reliability and integrity to both local and international partners.